NBP National Bank Jobs September 2026
NBP National Bank Jobs September 2026
Organization: NBP National Bank
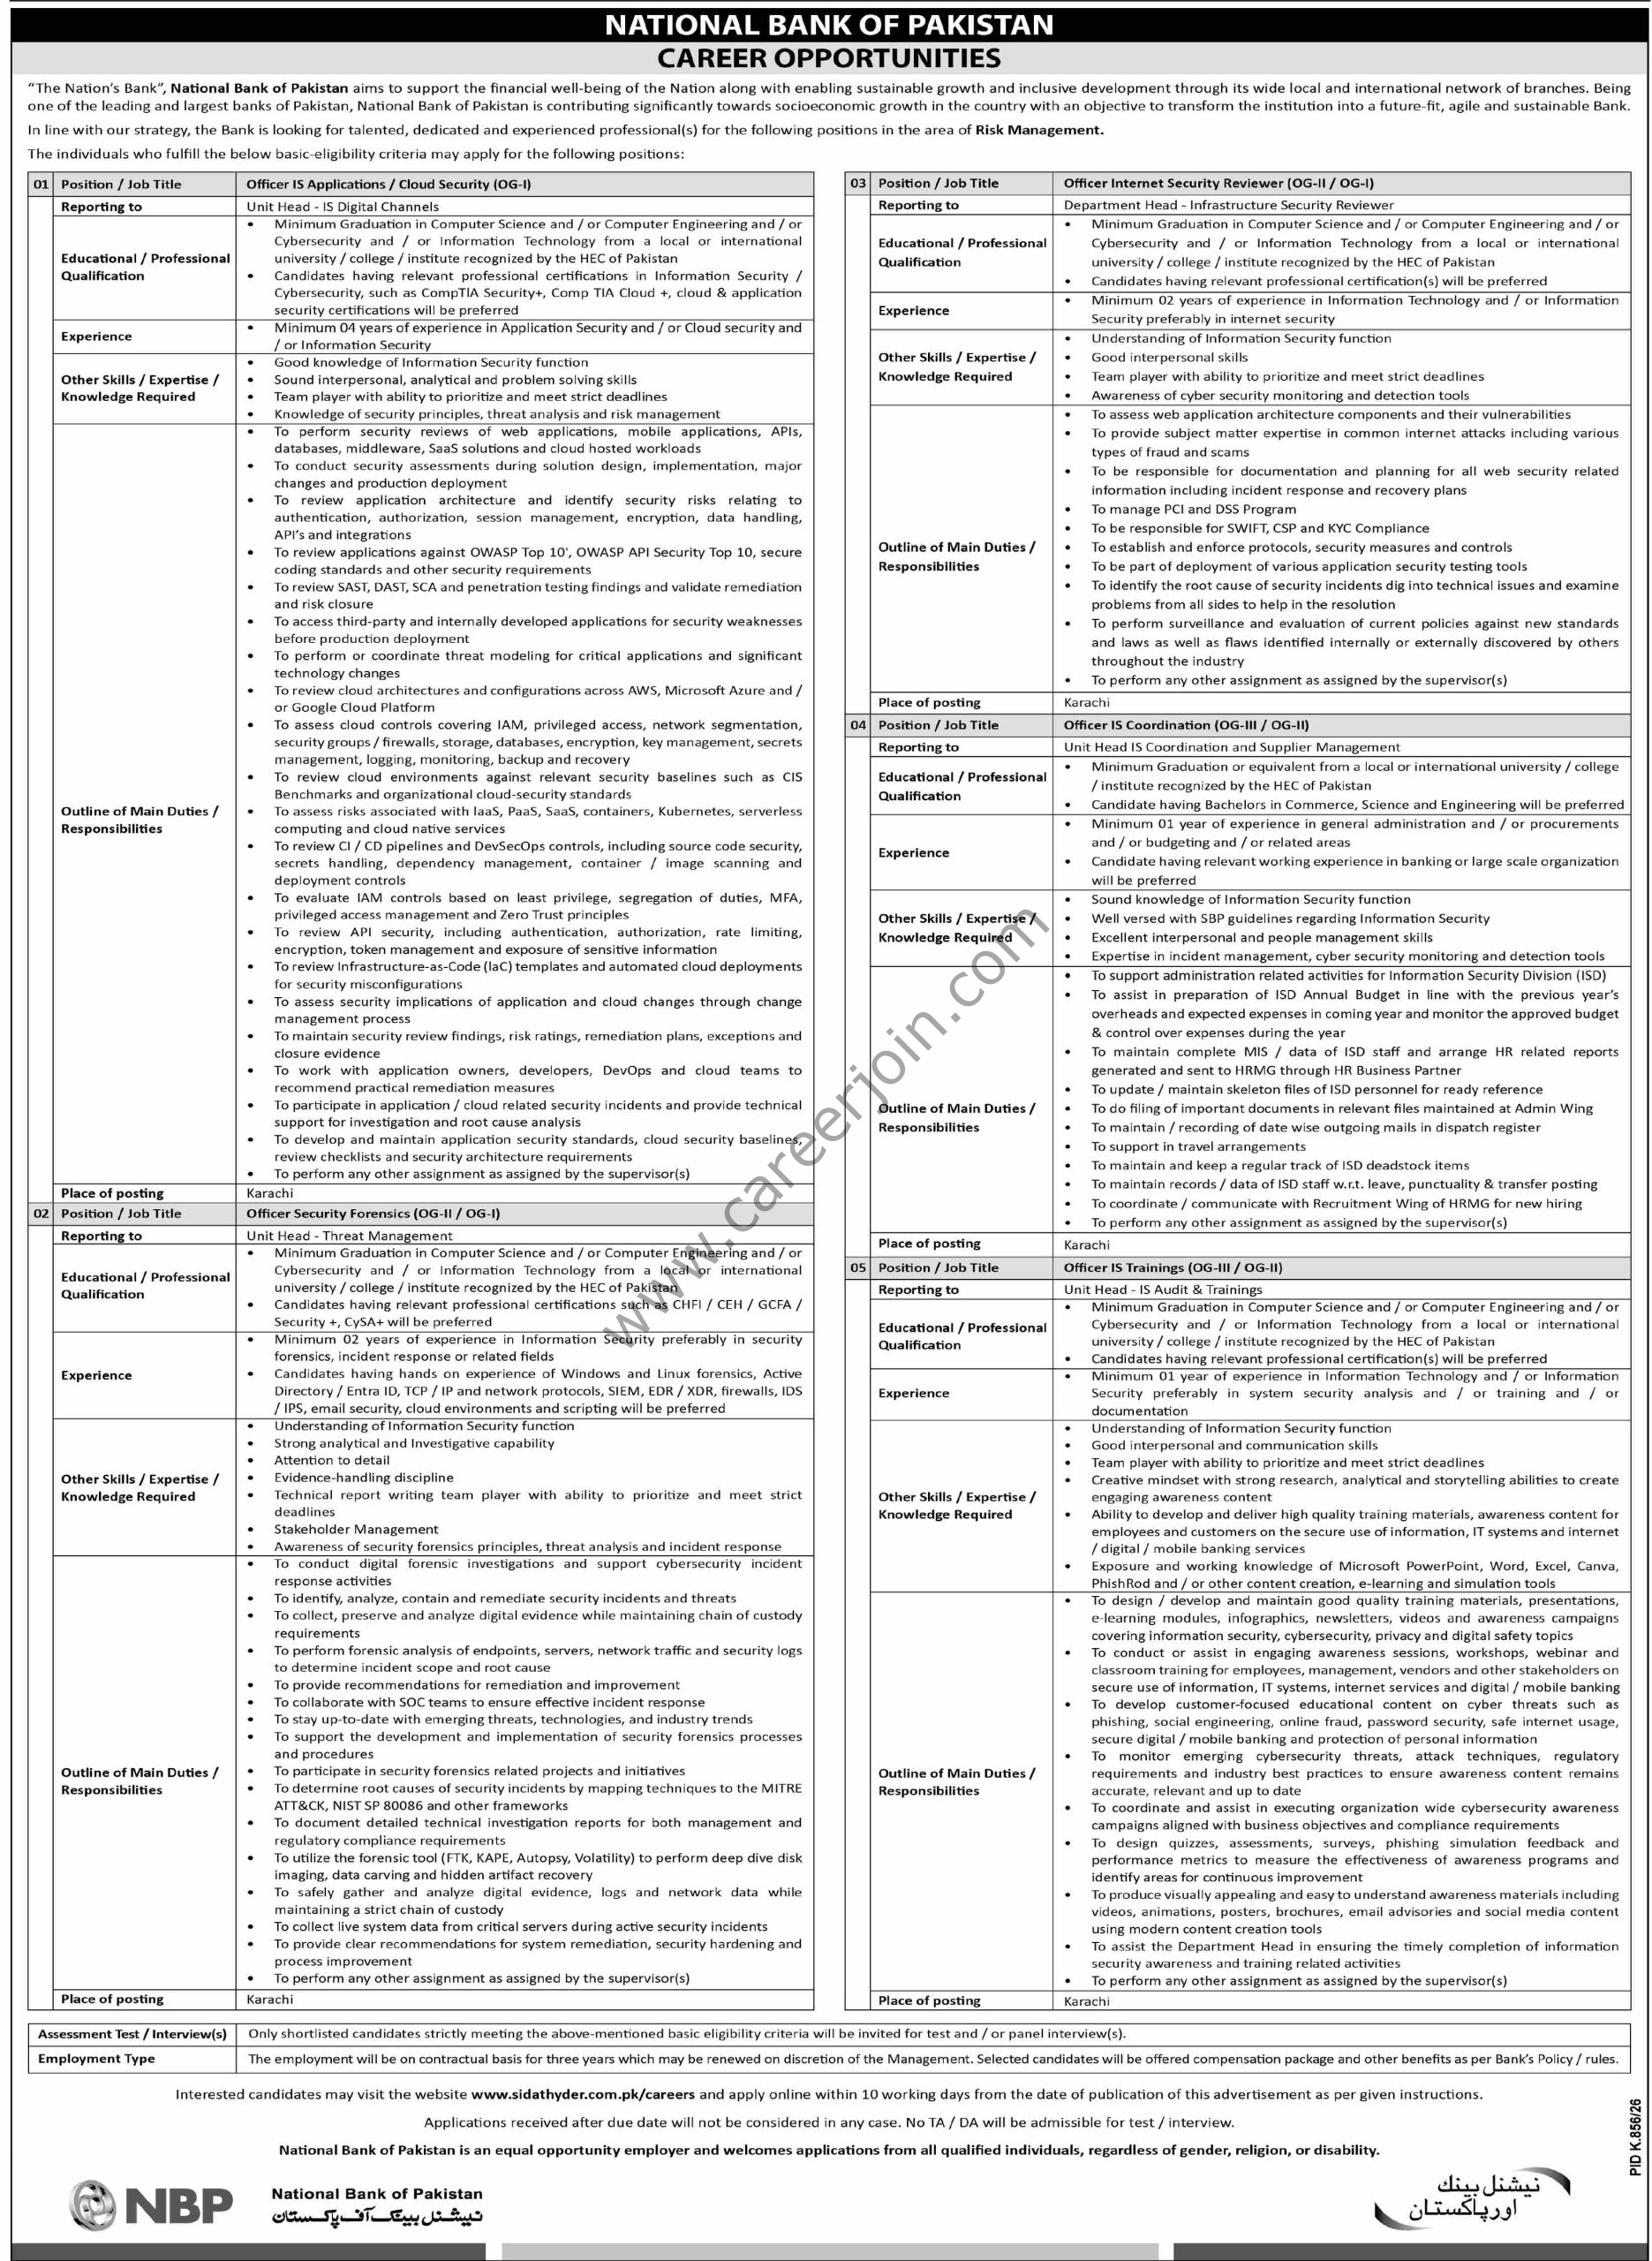
CAREER OPPORTUNITIES: “The Nation’s Bank”, National Bank of Pakistan aims to support the financial well-being of the Nation along with enabling sustainable growth and inclusive development through its wide local and international network of branches. Being one of the leading and largest banks of Pakistan, National Bank of Pakistan is contributing significantly towards socio-economic growth in the country with an objective to transform the institution into a future-fit, agile and sustainable Bank.
In line with our strategy, the Bank is looking for talented, dedicated and experienced professional(s) for the following positions in the area of Risk Management.
The individuals who fulfill the below basic eligibility criteria may apply for the following positions:
01 Position / Job Title: Officer IS Applications / Cloud Security (OG-II / OG-I)
Reporting to: Unit Head – IS Digital Channels
Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having relevant professional certifications in Information Security / Cybersecurity such as CompTIA Security+, Azure / AWS / Cloud, & cloud application security certifications will be preferred.
Experience:
- Minimum 02 years of experience in Application Security and / or Cloud Security and / or Information Security.
Other Skills / Expertise / Knowledge Required:
- Good knowledge of Information Security function.
- Strong interpersonal, analytical and problem-solving skills.
- Team player with ability to prioritize and meet strict deadlines.
- Knowledge of security principles, threat analysis and risk management.
- To perform security reviews of web applications, mobile applications, APIs, databases, middleware, SaaS solutions and cloud-hosted workloads.
- To conduct security assessments during solution design, implementation, code changes and production deployment.
- To review application access control and identity security rules relating to authentication, authorization, session management, encryption, data handling, APIs and integrations.
- To review applications against OWASP Top 10, OWASP API Security Top 10, secure coding standards and other security requirements.
- To review SAST, DAST, SCA and penetration testing findings and validate remediation and risk closure.
- To assess third-party and internally developed applications for security weaknesses before production deployment.
- To perform or coordinate threat modeling for critical applications and significant technology changes.
Outline of Main Duties / Responsibilities:
- To review cloud architectures and configurations across AWS, Microsoft Azure and / or Google Cloud Platform.
- To assess cloud controls covering IAM, privileged access, network segmentation, security groups / firewalls, storage, databases, encryption, key management, secrets management, logging, monitoring, backup and recovery.
- To review cloud environments against relevant security baselines such as CIS Benchmarks and organizational cloud security standards.
- To review security configured with SaaS, PaaS, IaaS, containers, serverless, microservices computing and cloud native services.
- To review CI / CD pipelines and DevSecOps controls, including source code security, secrets handling, dependency management, container / image scanning and deployment controls.
- To evaluate IAM controls based on least privilege, segregation of duties, MFA, privileged access management and Zero Trust principles.
- To review API security, including authentication, authorization, rate limiting, encryption, token management, and exposure of sensitive information.
- To review Infrastructure as Code (IaC) templates and automated cloud deployments for security misconfigurations.
- To assess security implications of operational and cloud changes through change management process.
- To maintain security review logs, risk ratings, remediation plans, exceptions and closure evidence.
- To work with application owners, developers, DevOps and cloud teams to recommend practical remediation measures.
- To participate in application / cloud related security incidents and provide technical support for investigation and root cause analysis.
- To develop and maintain application security standards, cloud security baselines, review checklists and security baseline requirements.
- To perform any other assignment as assigned by the supervisor(s).
Place of posting: Karachi
02 Position / Job Title: Officer Security Forensics (OG-II / OG-I)
Reporting to: Unit Head – Threat Management
Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having relevant professional certifications such as CHFI / CEH / GCFA / Security+ / CySA+ will be preferred.
Experience:
- Minimum 02 years of experience in Information Security preferably in security forensics, incident response or related fields.
- Candidates having hands-on experience of Windows and Linux forensics, Active Directory, endpoint security and network protocols, SIEM, EDR / XDR, firewalls, IDS / IPS, cloud security, cloud environments and scripting will be preferred.
Other Skills / Expertise / Knowledge Required:
- Understanding of Information Security Function.
- Strong analytical and investigative capability.
- Attention to detail.
- Evidence-handling discipline.
- Technical report writing; team player with ability to prioritize and meet strict deadlines.
- Stakeholder Management.
Outline of Main Duties / Responsibilities:
- Knowledge of security forensics principles, threat analysis and incident response.
- To conduct digital forensics investigations and support cybersecurity incident response activities.
- To identify, analyze, contain and remediate security incidents and threats.
- To collect, preserve and archive digital evidence while maintaining chain of custody requirements.
- To perform forensic analysis of endpoints, servers, network traffic and security logs to determine incident scope and root cause.
- To provide recommendations for remediation and improvement.
- To collaborate with SOC teams to isolate affected incident response.
- To assist with responding threats, technologies, and industry trends.
- To support the development and implementation of forensic processes and procedures.
- To participate in security reviews related to threats and incidents.
- To determine root causes of security incidents by mapping techniques to the MITRE ATT&CK, NIST SP 800-61 and other frameworks.
- To document detailed technical investigation reports for both management and regulatory compliance requirements.
- To utilize standard tools (FTK, EnCase, Autopsy, Volatility) to perform deep disk, memory, data parsing and hidden artifact recovery.
- To safely gather and analyze digital evidence, logs and network files while maintaining a strict chain of custody.
- To collect live system data from critical servers during active security incidents.
- To provide clear recommendations for system remediation, security hardening and process improvements.
- To perform any other assignment as assigned by the supervisor(s).
Place of posting: Karachi
03 Position / Job Title: Officer Infrastructure Security Reviewer (OG-II / OG-I)
Reporting to: Department Head – Infrastructure Security Reviewer
Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having relevant professional certification(s) will be preferred.
Experience:
- Minimum 02 years of experience in Information Technology and / or Information Security, preferably in a bank/institution.
Other Skills / Expertise / Knowledge Required:
- Understanding of Information Security Function.
- Great interpersonal skills.
- Team player with ability to prioritize and meet strict deadlines.
- Awareness of cyber security monitoring and detection tools.
Outline of Main Duties / Responsibilities:
- To assess web application architecture components and their vulnerabilities.
- To provide subject matter expertise in common cyber attacks including various types of fraud and spam.
- To be responsible for documentation and planning for all web security-related information including incident response and recovery plans.
- To manage PCI and DSS Program.
- To be responsible for SWIFT, CSP and NCC Compliance.
- To establish and enforce protocols, security measures and controls.
- To take part in deployment of various application security testing tools.
- To identify the root cause of security incidents dig into technical issues and examine problems from all sides to help in resolution.
- To perform surveillance and evaluation of current policies against new standards and best as well as those identified internally or externally discovered by others throughout the industry.
- To perform any other assignment as assigned by the supervisor(s).
Place of posting: Karachi
04 Position / Job Title: Officer IS Coordination (OG-III / OG-II)
Reporting to: Unit Head IS Coordination and Budget Management
Educational / Professional Qualification:
- Minimum Graduation or equivalent from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having Bachelor’s in Commerce, Science and Engineering will be preferred.
Experience:
- Minimum 01 year of experience in general administration and / or procurement and / or budgeting and / or related areas.
- Candidate having relevant working experience in banking or large scale organization will be preferred.
Other Skills / Expertise / Knowledge Required:
- Sound Knowledge of Information Security Function.
- Well versed with SBP guidelines regarding Information Security.
- Excellent interpersonal and people management skills.
- Experience in incident management, cybersecurity monitoring and detection tools.
Outline of Main Duties / Responsibilities:
- To support administration-related activities for Information Security Division (ISD).
- To assist in preparation of ISD Annual Budget in line with the previous year’s actual heads and expected occurrences in coming year and monitor the approved budget & control over expenses during the year.
- To maintain complete MIS / data of ISD staff and arrange HR-related reports generated and sent to HRG through Head of Department.
- To prepare / maintain selection files of ISD personnel for ready reference.
- Incharge of important documents in relevant files maintained as Admin Wing.
- To maintain recording of outward/inward routing mails in dispatch register.
- To support audit activities.
- To maintain comprehensive regular record of ISD hardware items.
- To maintain record / data of ISD staff leave, loss, punctuality & transfers posting.
- To coordinate / communicate with Procurement Wing of HRMG for forwarding.
- To perform any other assignment as assigned by the supervisor(s).
Place of posting: Karachi
05 Position / Job Title: Officer IS Trainings (OG-II / OG-I)
Reporting to: Head – IS Audit & Trainings
Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having relevant professional certification(s) will be preferred.
Experience:
- Minimum 01 year of experience in Information Technology and / or Information Security preferably in systemic security awareness and / or training unit / or department.
Other Skills / Expertise / Knowledge Required:
- Understanding of Information Security Function.
- Good interpersonal and communication skills.
- Team player with ability to prioritize and meet strict deadlines.
- Creative thinker with strong research, instructional design, and storytelling abilities to create engaging awareness content.
- Ability to design and deliver high quality training materials, awareness content to employees and customers on the secure use of information, IT systems and financial / digital / mobile banking services.
Outline of Main Duties / Responsibilities:
- Hands-on expertise and working knowledge of Microsoft PowerPoint, Word, Excel, Canva, Photoshop and LMS / interactive e-learning & learning simulation tools.
- To design / develop and maintain good quality training materials, presentations, e-learning modules, infographics, newsletters, videos and awareness campaigns covering information security, cybersecurity, privacy and digital safety topics.
- To conduct or assist in engaging awareness sessions, workshops, webinars and classroom training for employees, management, vendors and other stakeholders on secure use of Information, IT systems, Internet services and digital / mobile banking.
- To develop customer-focused educational content on cyber threats such as phishing, social engineering, smishing, password security, safe internet usage, secure digital / mobile banking and protection of personal information.
- To monitor emerging cybersecurity threats, attack techniques, regulatory requirements and industry best practices to ensure awareness content remains accurate, relevant, and updated.
- To coordinate and assist in executing organization-wide cybersecurity awareness campaigns aligned with business objectives and compliance requirements.
- To design quizzes, assessments, surveys, gathering feedback and performance metrics to measure the effectiveness of awareness programs and identify areas for continuous improvement.
- To produce visually appealing and easy to understand awareness materials including fliers, banners, posters, brochures, email advisories and social media content using modern content creation tools.
- To assist the Department Head in ensuring the timely completion of information security awareness and training requirements.
- To perform any other assignment as assigned by the supervisor(s).
Place of posting: Karachi
Assessment Test / Interview(s): Only shortlisted candidates strictly meeting the above-mentioned basic eligibility criteria will be invited for test and / or panel interview(s).
Employment Type: The employment will be on contractual basis for three years which may be renewed at discretion of the Management. Selected candidates will be offered compensation package and other benefits as per Bank’s Policy / rules.
Interested candidates may visit the website https://www.sidathyder.com.pk/careers and apply online within 10 working days from the date of publication of this advertisement as per given instructions.
Applications received after due date will not be considered in any case. No TA / DA will be admissible for test / interview.
National Bank of Pakistan is an equal opportunity employer and welcomes applications from all qualified individuals, regardless of gender, religion, or disability.
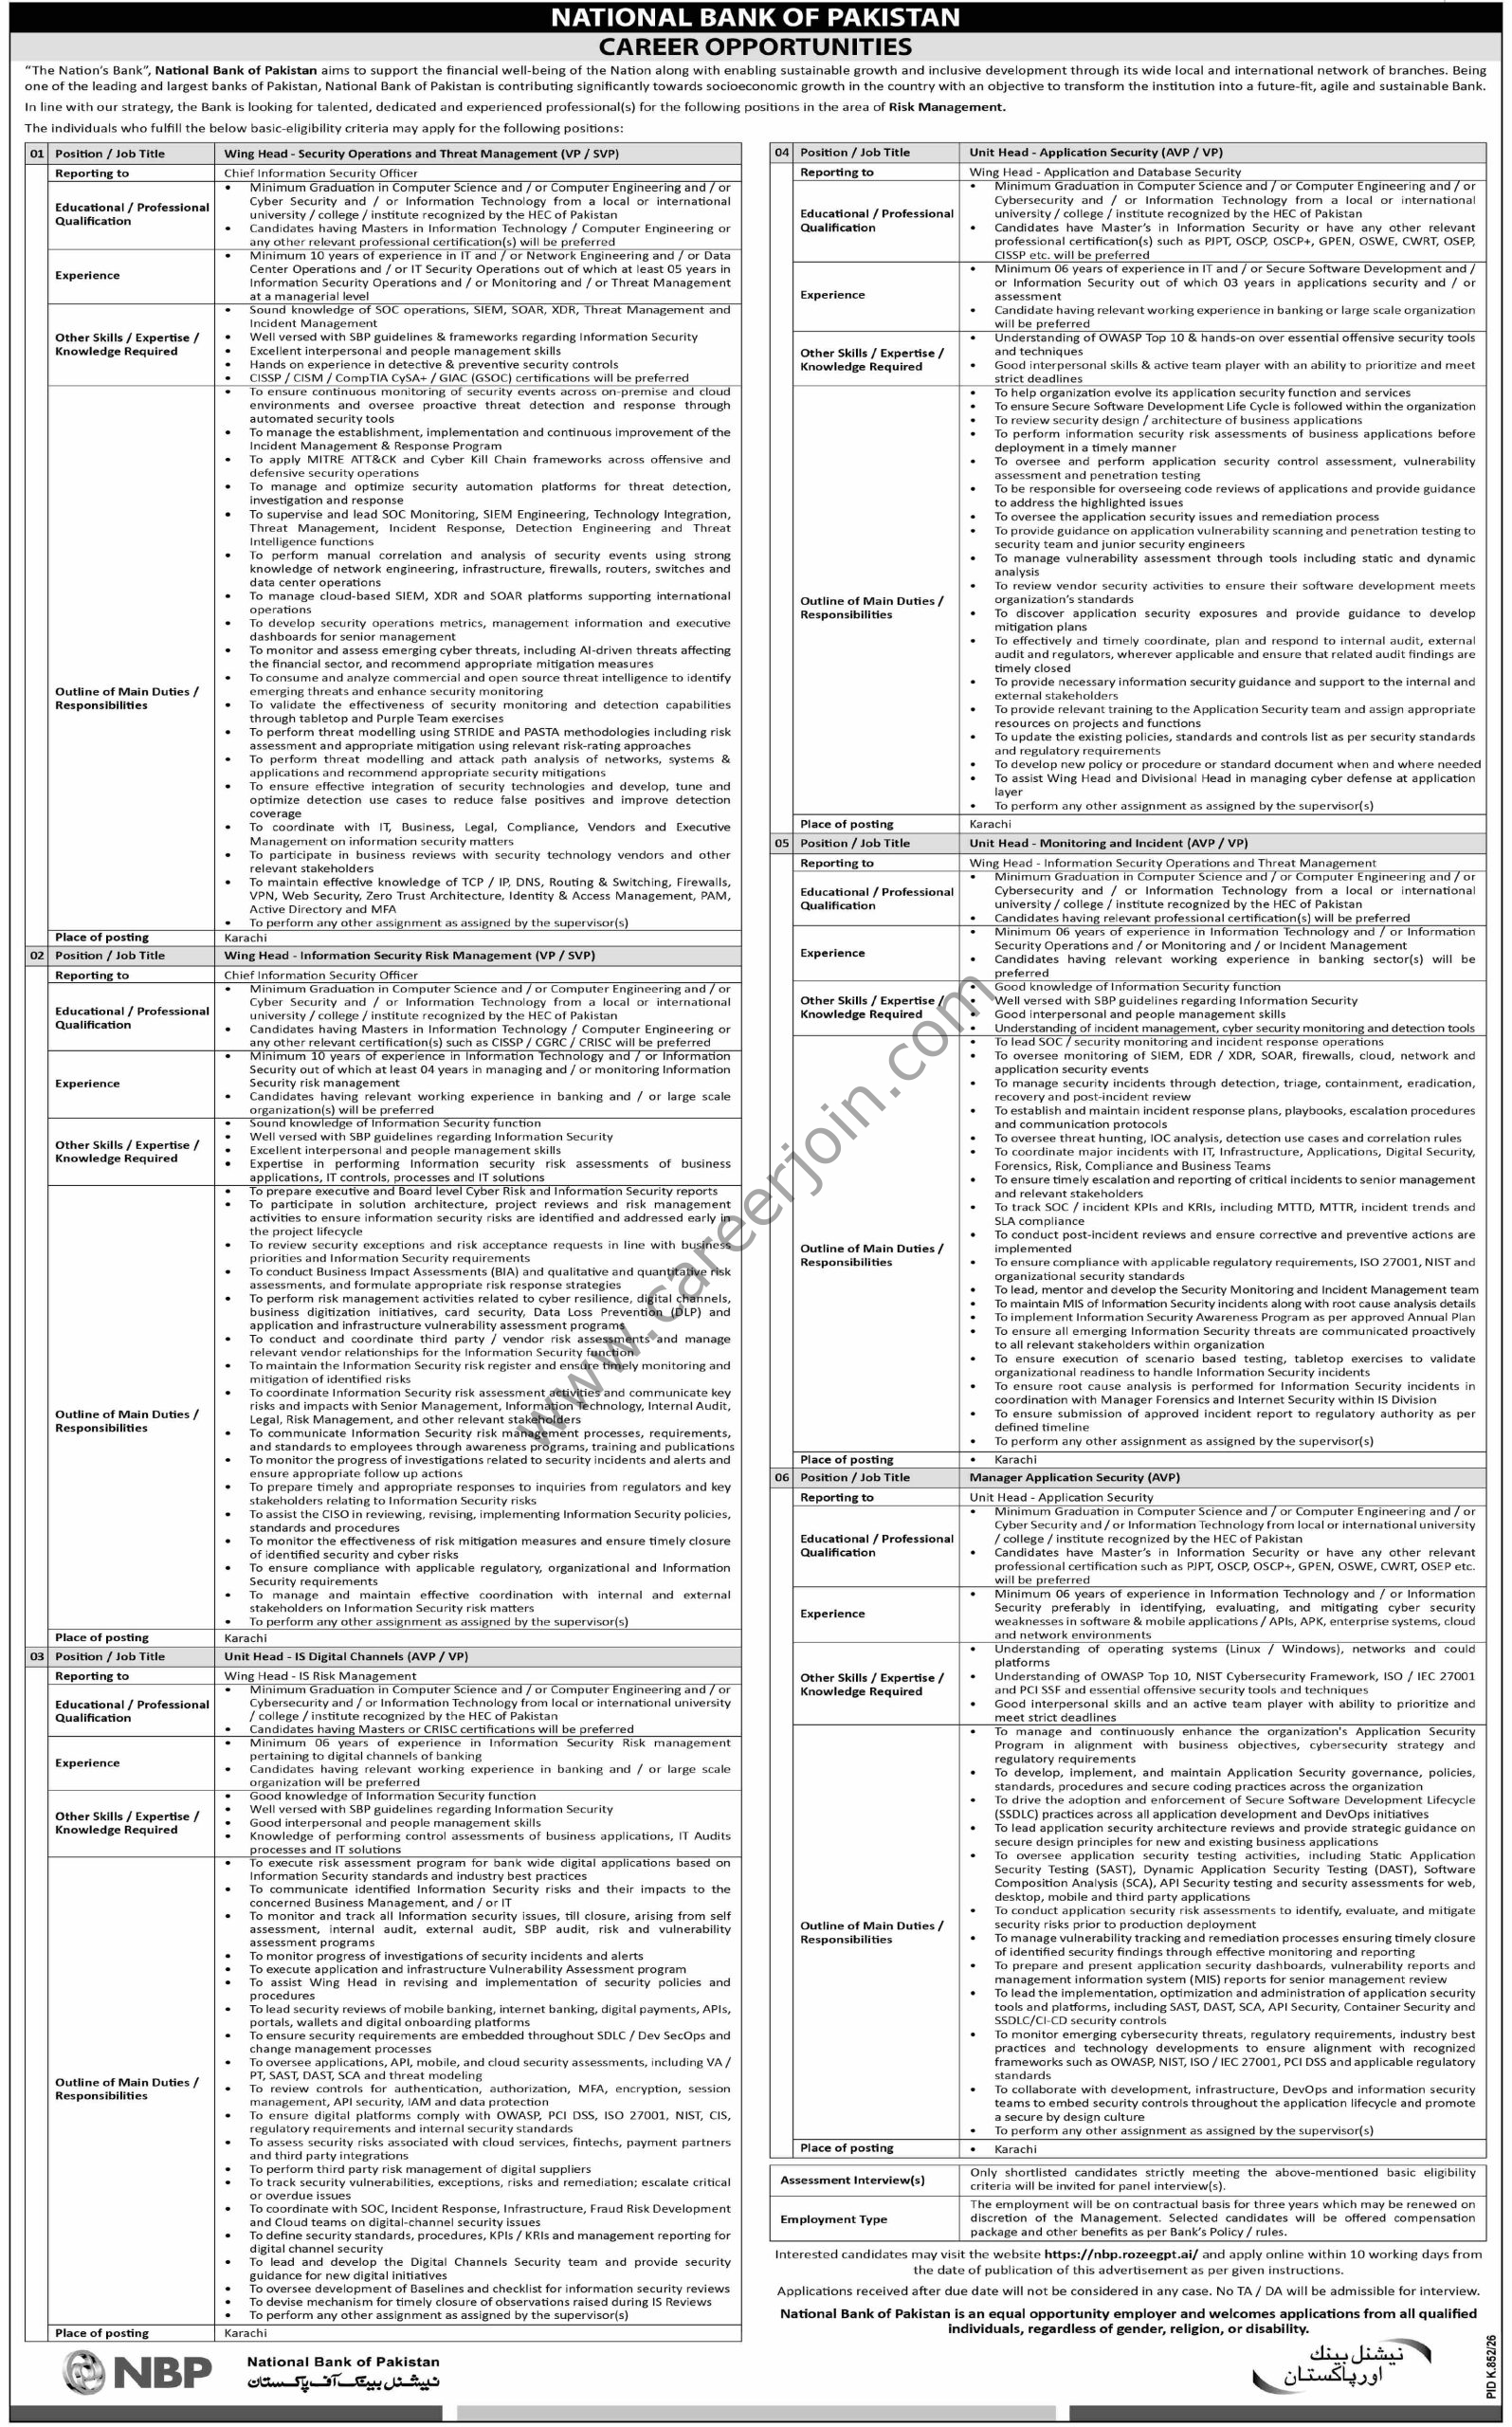
CAREER OPPORTUNITIES: “The Nation’s Bank”, National Bank of Pakistan aims to support the financial well-being of the Nation along with enabling sustainable growth and inclusive development through its wide local and international network of branches. Being one of the leading and largest banks of Pakistan, National Bank of Pakistan is contributing significantly towards socio-economic growth in the country with an objective to transform the institution into a future-fit, agile and sustainable Bank.
In line with our strategy, the Bank is looking for talented, dedicated and experienced professional(s) for the following positions in the area of Risk Management.
The individuals who fulfill the below basic eligibility criteria may apply for the following positions:
01 Position / Job Title: Wing Head – Security Operations and Threat Management (AVP / VP)
Reporting to: Chief Information Security Officer
Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having Master’s in Information Security / Computer Engineering or any other relevant professional certification(s) will be preferred.
Experience:
- Minimum 05 years of experience in IT and / or Network Engineering and / or Data Security out of which at least 03 years in managing, leading and supervising Information Security Operations and / or Monitoring and / or Threat Management at managerial level.
- Hands-on experience with SIEM, EDR, SOAR, XDR, Threat Management and incident response tools.
Other Skills / Expertise / Knowledge Required:
- Well versed with SBP guidelines and standards regarding Information Security.
- Excellent interpersonal and people management skills.
- Hands-on experience in Detection & Incident Response domain.
- CISM / CISA / CISSP / CompTIA Security+ / CEH / GCIA / GCIH certifications will be preferred.
Outline of Main Duties / Responsibilities:
- To develop and implement strategies to prevent security breaches across enterprise and cloud environments, with focus on proactive threat detection and response, high estimated security incidents.
- To manage the establishment, implementation and continuous improvement of the Security Operations and Incident Response program.
- To apply MITRE ATT&CK and Cyber Kill Chain frameworks across defensive and offensive security operations.
- To manage and optimize security automation platforms for threat detection, incident response, and containment.
- To supervise and lead SOC Monitoring, Threat Engineering, Threat Intelligence, Threat Management, Incident Response, Detection Engineering and Threat Hunting activities / teams.
- To perform manual correlation and analysis of security events using deep knowledge of network engineering, infrastructure, firewalls, routers, endpoint and data center operations.
- To operate coordinated SIEM, XDR and SOAR platforms supporting international operations.
- To develop security operations metrics, management dashboards and vulnerability reports for CISO and senior leadership.
- To monitor and analyze emerging cyber threats, including AI-driven threats affecting the financial sector, and recommend appropriate mitigation measures.
- To consume and customize commercial and open-source threat intelligence feeds to strengthen local threat detection and containment mechanisms.
- To validate the effectiveness of security monitoring and detection capabilities through Red team and Purple Team exercises.
- To perform threat modeling using STRIDE and PASTA methodologies including risk assessment and appropriate mitigation integrated into engineering workflows.
- To perform threat modeling and attack path analysis of networks, systems and applications to design and recommend appropriate security controls.
- To review SIEM, EDR and XDR alerts to continually tune and develop, fine-tune detection rules and use cases to reduce false positives and improve detection efficacy.
- To coordinate with IT Business, Legal, Compliance, Vendors and Executive Management on information security matters.
- To participate in business reviews with security technology vendors and other third-party providers.
- To maintain effective knowledge of TCP / IP, DNS, Routing & Switching, Firewalls, VPN, Web Security, Zero Trust Architecture, Identity & Access Management, PAM, Active Directory and IAM.
- To perform any other assignment as assigned by the supervisor(s).
Place of posting: Karachi
02 Position / Job Title: Wing Head – Information Security Risk Management (VP / SVP)
Reporting to: Chief Information Security Officer
Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having Masters in Information Technology / Computer Engineering or any other relevant certification(s) like CISM / CISA / CRISC will be preferred.
Experience:
- Minimum 08 years of experience in Information Technology and / or Information Security, out of which at least 04 years in managing, and / or monitoring Information Security risk management.
- Candidates having relevant working experience in banking and / or large scale organization(s) will be preferred.
Other Skills / Expertise / Knowledge Required:
- Sound knowledge of Information Security function.
- Well versed with SBP regulations regarding Information Security.
- Excellent interpersonal and people management skills.
- Expertise in performing information security risk assessments of banking applications, IT products, and vendor systems.
Outline of Main Duties / Responsibilities:
- To provide executive-level and Board-level Cyber Risk profiles and security reports.
- To participate in solution architecture, project reviews and risk management activities to ensure information security risks are identified and addressed early in the project lifecycle.
- To review security exceptions and risk acceptance requests in line with business priority and Information Security requirements.
- To conduct gap analysis against standards like NIST, ISO 27001, and perform risk assessments, and formulate appropriate risk response strategies.
- To perform risk management activities related to cyber resilience, digital channels, payment technology platforms, core banking, cloud security risk, third-party risk, application and infrastructure vulnerability assessment programs.
- To conduct and coordinate third party / vendor risk assessments and manage inherent vendor relationships for the Information Security function.
- To manage the Information Security risk register and ensure timely tracking and mitigation of identified risks.
- To coordinate Information Security risk assessment activities and communicate key risks and recommendations to management, Information Technology, Head of Audit, Legal, Risk Management, and other relevant stakeholders.
- To communicate Information Security Risk Management processes, requirements, and standards to employees through awareness programs, training and instructions.
- To monitor the progress of investigations related to security incidents and plan and ensure appropriate follow-up actions.
- To prepare timely and appropriate response to inquiries from regulatory bodies, internal audit, external audit, and statutory bodies.
- To assist the CISO in developing, reviewing, and updating Information Security policies, standards, and procedures.
- To monitor the implementation of risk mitigation measures and ensure timely closure of identified risk elements and audit observations.
- To maintain compliance with applicable regulatory, organizational and information security requirements.
- To manage and maintain effective coordination with internal and external stakeholders on Information Security risk matters.
- To perform any other assignment as assigned by the supervisor(s).
Place of posting: Karachi
03 Position / Job Title: Unit Head – IS Digital Channels (AVP / VP)
Reporting to: Wing Head – Digital Security
Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having Masters / CISM / CISSP certification will be preferred.
Experience:
- Minimum 06 years of experience in Information Security Risk Management pertaining to digital channels of banking.
- Candidates having relevant working experience in banking and / or large scale organization will be preferred.
Other Skills / Expertise / Knowledge Required:
- Sound knowledge of Information Security function.
- Well versed with SBP guidelines regarding Information Security.
- Great interpersonal and people management skills.
- Knowledge of performing security assessments of banking applications, IT Audit and regulatory compliance requirements.
Outline of Main Duties / Responsibilities:
- To manage risk assessment processes for bank-wide digital applications based on Information Security standards and industry best practices.
- To assess risks related to emerging cyber security risks and their impacts on the enterprise Business Management, and IT.
- To monitor and track implementation, security issues, risk closure, arising from self assessments, IS audits, external audits, SBP audit, risk and vulnerability assessment programs.
- To monitor progress of investigations of security incidents and threats.
- To manage application and infrastructure Vulnerability Assessment programs.
- To provide advice, assistance in drafting and implementation of security policies and procedures.
- To conduct security reviews of mobile banking, internet banking, digital payments, APIs, and associated technology infrastructure across all phases.
- To ensure security requirements are embedded throughout SDLC / DevSecOps and change management processes.
- To review application security, website, and cloud security assessments, including SAST / DAST, SCA, Zero Trust and threat modeling.
- To evaluate controls for authentication, authorization, MFA, encryption, token management, session security, and API security.
- To align digital platforms security with OWASP, PCI DSS, ISO 27001, NIST, SBP regulatory requirements, and internal security standards.
- To assess security risks associated with cloud services, FinTech, payment systems, and third-party integrations.
- To perform third party risk management of digital platforms.
- To track security vulnerabilities, exceptions, risks, and remediation, navigate critical vulnerabilities.
- To coordinate with SOC, Incident Response, Infrastructure, Fraud Risk Management, and DevSecOps teams on digital channel security risks.
- To refine security standards, procedures, KRI / KPI, risk management reporting for digital channel security.
- To lead and develop the Digital Channels Security team and provide security guidance for new digital initiatives.
- To oversee development of baselines and checklist for application security reviews.
- To design mechanisms for timely closure of observation noted during IS Reviews.
- To perform any other assignment as assigned by the supervisor(s).
Place of posting: Karachi
04 Position / Job Title: Unit Head – Application Security (AVP / VP)
Reporting to: Wing Head – Application and Security
Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having Masters in Information Security or have any other relevant professional certification(s) such as CEH, OSCP, OSWE, GWAPT, CWE, CISSP, CISM, etc. will be preferred.
Experience:
- Minimum 06 years of experience in IT and / or Software Development and / or Information Security out of which 03 years in application security and / or assessment.
- Candidates having relevant working experience in banking or large scale organization will be preferred.
Other Skills / Expertise / Knowledge Required:
- Understanding of OWASP Top 10, hands-on experience of offensive security tools and techniques.
- Great interpersonal skills & positive team player with an ability to prioritize and meet strict deadlines.
- To lead organization-wide application security functions and services.
- To establish application security standards, baselines and policies across the organization.
- To review security design / architecture of business applications.
- To perform information security risk assessments of business applications before deployment in a timely manner.
- To oversee and manage dynamic application security controls assessment, vulnerability assessment and penetration testing.
- To be responsible for overseeing code reviews of applications and provide guidance to developers on remediation.
Outline of Main Duties / Responsibilities:
- To manage the application security review and assessment process.
- To provide guidance on application vulnerability scanning and penetration testing for internal and partner security assessments.
- To manage vulnerability assessment through tools including static and dynamic analysis.
- To review vendor security activities to ensure their software development meets internal security standards.
- To discover application security weaknesses and provide guidance to developers to remediate risks.
- To effectively and timely coordinate, plan and respond to internal audit, external audit, and SBP inspection findings, wherever applicable and ensure that detailed findings are timely closed.
- To provide necessary information security guidance and support to the internal and external stakeholders.
- To provide functional input for Application Security team, and assign appropriate resources for projects and functions.
- To update the existing policies, standards and controls as per security standards, best practices and regulatory guidance.
- To develop new policy or procedure or standard document when and where needed.
- To assist Wing Head and Division Head in managing cyber defense at application level.
- To perform any other assignment as assigned by the supervisor(s).
Place of posting: Karachi
05 Position / Job Title: Unit Head – Monitoring and Incident (AVP / VP)
Reporting to: Wing Head – Information Security Operations and Threat Management
Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having Masters in Information Security will be preferred.
Experience:
- Minimum 06 years of experience in Information Technology and / or Information Security, out of which 03 years in Monitoring and Incident Management.
- Candidates having relevant working experience in banking sector will be preferred.
Other Skills / Expertise / Knowledge Required:
- Good knowledge of Information Security function.
- Well versed with SBP guidelines regarding Information Security.
- Good interpersonal and people management skills.
- Understanding of incident management, cyber security monitoring and detection tools.
Outline of Main Duties / Responsibilities:
- To lead and manage the SOC Team for Monitoring and Incident Response.
- To oversee monitoring of SIEM, EDR / XDR, SOAR, firewalls, cloud, network and application security controls.
- To manage security incidents through collection, triage, containment, eradication, recovery and post-incident analysis.
- To establish and maintain incident response plans, playbooks, escalation procedures and communication protocols.
- To evaluate incident analysis, detection, use cases and correlation rules.
- To coordinate major incidents with IT, Infrastructure, Applications, Digital Security, Forensics, Risk, Compliance and Business Teams.
- To ensure timely notification and reporting of critical incidents to senior management and regulators.
- To track DST / Incident KPI and KPIs, including MTTR, MTTD, incident trends, and root cause analysis.
- To lead post-incident review and ensure corrective and preventive actions are implemented.
- To ensure compliance with applicable regulatory requirements, ISO 27001, NIST, and organizational security standards.
- To lead and manage 24/7 Security Operations Center (SOC) Security Monitoring and Incident Management Team.
- To maintain MIS of information security incidents along with root cause analysis details.
- To implement Information Security Awareness Program as per approved Annual Plan.
- To assist in preparing Information Security bulletins and communicate periodically to all business functions within organization.
- To manage execution of scenario-based testing, Tabletop exercises to validate organization readiness to handle Information Security Incidents.
- To conduct post-incident reviews to identify lessons learned and prevent re-incidents in coordination with Management Response Team and IT teams within the Bank.
- To ensure submission of approved incident report to regulatory authority as per regulatory timelines.
- To perform any other assignment as assigned by the supervisor(s).
Place of posting: Karachi
06 Position / Job Title: Manager Application Security (AVP)
Reporting to: Unit Head – Application Security
Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having Master’s in Information Security or have any other relevant professional certification such as CISA, CISSP, CISM, CEH, GWAPT, CWE, OSCP, OSWE, etc. will be preferred.
Experience:
- Minimum 05 years of experience in Information Technology and / or Information Security, preferably in identifying, evaluating, and mitigating cybersecurity risks / vulnerabilities in software & mobile applications / APIs, Application architecture, and source code level.
Other Skills / Expertise / Knowledge Required:
- Understanding of operating systems (Linux / Windows), networks and cloud platforms.
- Knowledge of OWASP Top 10, NIST Cybersecurity Framework, ISO / IEC 27001 and PCI DSS and code review techniques / tools.
- Good interpersonal skills and an active team player with ability to prioritize and meet strict deadlines.
Outline of Main Duties / Responsibilities:
- To drive and maintain application security governance, policies, standards, processes and secure coding practices across the organization.
- To foster the adoption and enhancement of Secure Software Development Lifecycle (SSDLC) practices across all application development and DevOps workflows.
- To perform application design / architecture review and provide design guidance on secure design principles for new and existing business applications.
- To manage application security testing activities, including Static Application Security Testing (SAST), Dynamic Application Security Testing (DAST), Software Composition Analysis (SCA), API security testing and security assessments for web, desktop, mobile and third-party applications.
- To conduct application security risk assessments to identify, evaluate, and mitigate risks associated with software applications.
- To manage vulnerability tracking and remediation processes, ensuring timely closure of identified security findings through verification testing and re-testing.
- To track, analyze, and report application security metrics, vulnerability trends, and management information system (MIS) reports for senior management.
- To lead the implementation, administration and administration of application security tools and platforms, including SAST, DAST, SCA, API Security, Container Security and Code Review tools.
- To monitor emerging cybersecurity threats, regulatory requirements, industry best practices and technology developments to ensure alignment with recognized standards such as OWASP, NIST, ISO / IEC 27001, PCI DSS and applicable regulatory mandates.
- To collaborate with development, infrastructure, DevOps and information security teams to embed security controls throughout the application lifecycle and promote a strong security culture.
- To perform any other assignment as assigned by the supervisor(s).
Place of posting: Karachi
Assessment Test / Interview(s): Only shortlisted candidates strictly meeting the above-mentioned basic eligibility criteria will be invited for panel interview(s).
Employment Type: The employment will be on contractual basis for three years which may be renewed on discretion of the Management. Selected candidates will be offered compensation package and other benefits as per Bank’s Policy / rules.
Interested candidates may visit the website https://www.sidathyder.com.pk/careersand apply online within 10 working days from the date of publication of this advertisement as per given instructions.
Applications received after due date will not be considered in any case. No TA / DA will be admissible for test / interview.
National Bank of Pakistan is an equal opportunity employer and welcomes applications from all qualified individuals, regardless of gender, religion, or disability.
Published Date: 13 September 2026
Newspaper: Dawn
NBP National Bank Jobs September 2026


Jobs By Cities
Jobs By Field
Jobs By Organization
