National Bank NBP Jobs September 2026
National Bank NBP Jobs September 2026
Organization: National Bank of Pakistan NBP
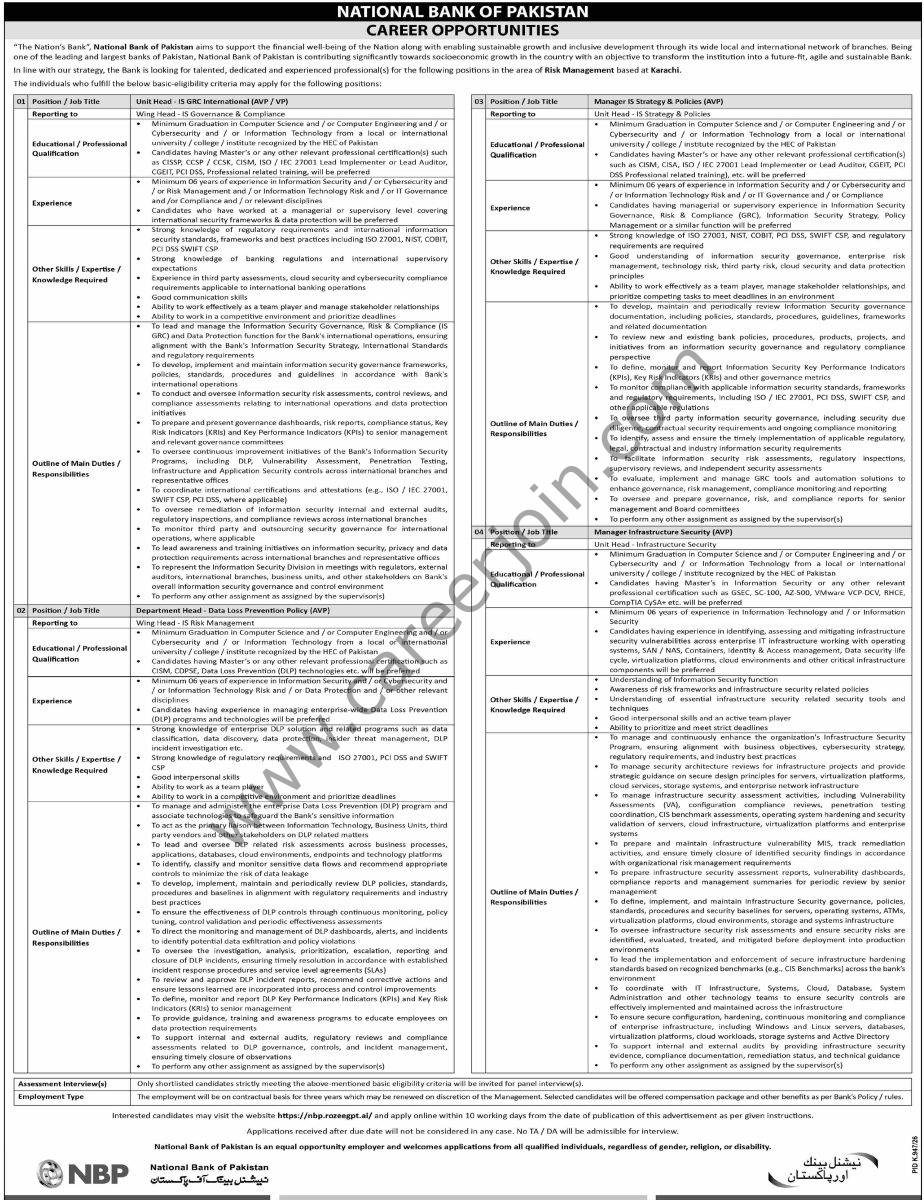
CAREER OPPORTUNITIES: “The Nation’s Bank”, National Bank of Pakistan aims to support the financial well-being of the Nation along with enabling sustainable growth and inclusive development through its wide local and international network of branches. Being one of the leading and largest banks of Pakistan, National Bank of Pakistan is contributing significantly towards socioeconomic growth in the country with an objective to transform the institution into a future-fit, agile and sustainable Bank. In line with our strategy, the Bank is looking for talented, dedicated and experienced professionals for the following positions in the area of Risk Management based at Karachi.
The individuals who fulfill the below basic eligibility criteria may apply for the following positions:
01 Position / Job Title: Unit Head – IS GRC International (AVP / VP)
- Reporting to: Wing Head – IS Governance & Compliance
- Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having Master’s or any other relevant professional certification(s) such as CISA, CISM, CGEIT, CISSP, ISO / IEC 27001 Lead Implementer or Lead Auditor, CGEIT, PCI DSS Professional related training, will be preferred.
- Experience:
- Minimum 06 years of experience in Information Security and / or Cybersecurity and / or Risk Management and / or Information Technology Risk and / or IT Governance and / or Compliance and / or Discipline.
- Candidates who have worked at a managerial or supervisory level involving international security frameworks & data protection will be preferred.
- Other Skills / Expertise / Knowledge Required:
- Strong knowledge of regulatory requirements and international information security standards, frameworks and best practices including ISO 27001, NIST, COBIT, PCI DSS, SWIFT, CSP.
- Strong knowledge of banking regulations and international supervisory expectations.
- Experience in third party assessments, cloud security and cybersecurity compliance requirements applicable to international banking operations.
- Good communication skills.
- Ability to work effectively as a team player and manage stakeholder relationships.
- Ability to work in a competitive environment and prioritize deadlines.
- Outline of Main Duties / Responsibilities:
- To lead and manage the Information Security Governance, Risk & Compliance (IS GRC) and Data Protection function for the Bank’s International operations, ensuring alignment with the Bank’s Information Security Strategy, International Standards and regulatory requirements.
- To develop, implement and maintain information security governance frameworks, policies, standards, procedures and guidelines in accordance with Bank’s international operations.
- To conduct and oversee information security risk assessments, control reviews, and compliance assessments relating to international operations and data protection initiatives.
- To prepare and present governance dashboards, risk reports, compliance status, Key Risk Indicators (KRIs) and Key Performance Indicators (KPIs) to senior management and relevant governance committees.
- To oversee continuous improvement initiatives of the Bank’s Information Security Program, including Vulnerability Assessment, Penetration Testing, Infrastructure and Application Security controls across international branches and representative offices.
- To coordinate international certifications and attestations (e.g., ISO / IEC 27001, SWIFT CSP, PCI DSS, where applicable).
- To oversee remediation of information security internal and external audits, regulatory inspections, and compliance reviews across international branches.
- To monitor third party and outsourcing security governance for international operations, where applicable.
- To lead compliance and steering elements of Information Security, privacy and data protection requirements across international branches and representative offices.
- To represent the Information Security Division in meetings with regulators, external auditors, international branches, business units, and other stakeholders on Bank’s overall information security governance and control environment.
- To perform any other assignment as assigned by the supervisor(s).
02 Position / Job Title: Department Head – Data Loss Prevention Policy (AVP)
- Reporting to: Wing Head – IS Risk Management
- Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having Master’s or any other relevant professional certification such as CISM, CDPSE, Data Loss Prevention (DLP) technologies etc. will be preferred.
- Experience:
- Minimum 05 years of experience in Information Security and / or Cybersecurity and / or Information Technology Risk and / or Data Protection and / or other relevant disciplines.
- Candidates having experience in managing enterprise-wide Data Loss Prevention (DLP) programs and technologies will be preferred.
- Other Skills / Expertise / Knowledge Required:
- Strong knowledge of enterprise DLP solution and related programs such as data classification, data discovery, data protection, insider threat management, DLP incident investigation, etc.
- Strong knowledge of regulatory requirements and ISO 27001, PCI DSS and SWIFT CSP.
- Good interpersonal skills.
- Ability to work as a team player.
- Ability to work in a competitive environment and prioritize deadlines.
- Outline of Main Duties / Responsibilities:
- To manage and administer the enterprise Data Loss Prevention (DLP) program and associated technologies to safeguard the Bank’s sensitive information.
- To act as the primary liaison between Information Technology, Business Units, Third Party Vendors and other stakeholders on DLP-related matters.
- To lead and oversee DLP-related risk assessments across business processes, applications, databases, cloud environments, endpoints and technology platforms.
- To identify, classify and monitor sensitive data flows and recommend appropriate controls to mitigate data loss risks.
- To develop, implement, maintain and periodically review DLP policies, standards, procedures and baselines in alignment with regulatory requirements and industry best practices.
- To ensure the effectiveness of DLP controls through continuous monitoring, policy tuning, control validation and periodic effectiveness assessments.
- To direct the monitoring and management of DLP dashboards, alerts, and incidents to prevent potential data exfiltration and policy violations.
- To oversee the investigation, analysis, prioritization, escalation, reporting and closure of DLP incidents, ensuring timely resolution in accordance with established incident response procedures and service level agreements (SLAs).
- To review and approve DLP incident reports, recommend corrective actions and ensure lessons learned are incorporated into process and control improvements.
- To define, monitor and report Key Performance Indicators (KPIs) and Key Risk Indicators (KRIs) to senior management.
- To provide guidance, training and awareness programs to educate employees on data protection requirements.
- To support internal and external audits, regulatory reviews and compliance assessments related to DLP governance, controls, and incident management, ensuring timely closure of observations.
- To perform any other assignment as assigned by the supervisor(s).
03 Position / Job Title: Manager IS Strategy & Policies (AVP)
- Reporting to: Unit Head – IS Strategy & Policies
- Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having Master’s or any other relevant professional certification(s) such as CISM, CISA, ISO / IEC 27001 Lead Implementer or Lead Auditor, CGEIT, PCI DSS Professional related training, etc. will be preferred.
- Experience:
- Minimum 05 years of experience in Information Security and / or Cybersecurity and / or Information Technology Risk and / or IT Governance and / or Compliance.
- Candidates having managerial or supervisory experience in Information Security Governance, Risk & Compliance (GRC), Information Security Strategy, Policy Management or a similar function will be preferred.
- Other Skills / Expertise / Knowledge Required:
- Strong knowledge of ISO 27001, NIST, COBIT, PCI DSS, SWIFT CSP, and regulatory requirements are required.
- Good understanding of information security governance, enterprise risk management, technology risk, third party risk, cloud security and data protection principles.
- Ability to work effectively as a team player, manage stakeholder relationships, and prioritize competing tasks to meet deadlines in an environment.
- Outline of Main Duties / Responsibilities:
- To develop, maintain and periodically review Information Security governance documentation, including policies, standards, procedures, guidelines, frameworks and related documentation.
- To review new and existing bank policies, procedures, products, projects, and initiatives from an information security governance and regulatory compliance perspective.
- To define, monitor and report Information Security Key Performance Indicators (KPIs), Key Risk Indicators (KRIs) and other governance metrics.
- To monitor compliance with applicable information security standards, frameworks and regulatory requirements, including ISO / IEC 27001, PCI DSS, SWIFT CSP, and other applicable regulations.
- To oversee third party information security governance, including security due diligence, contractual security requirements and ongoing compliance monitoring.
- To identify, assess and ensure the timely implementation of applicable regulatory, legal, contractual and industry information security requirements.
- To facilitate information security risk assessments, regulatory inspections, supervisory reviews and independent security assessments.
- To evaluate, implement and manage GRC tools and automation solutions to enhance governance, risk management, compliance monitoring and reporting.
- To oversee and prepare governance, risk, and compliance reports for senior management and Board committees.
- To perform any other assignment as assigned by the supervisor(s).
04 Position / Job Title: Manager Infrastructure Security (AVP)
- Reporting to: Unit Head – Infrastructure Security
- Educational / Professional Qualification:
- Minimum Graduation in Computer Science and / or Computer Engineering and / or Cybersecurity and / or Information Technology from a local or international university / college / institute recognized by the HEC of Pakistan.
- Candidates having Master’s in Information Security or any other relevant professional certification such as CISSP, CISM, AZ-500, VMware VCP-NV, AWS, CompTIA CySA+, etc. will be preferred.
- Experience:
- Minimum 05 years of experience in Information Technology and / or Information Security.
- Candidates having experience in identifying, assessing and mitigating infrastructure security vulnerabilities across enterprise IT infrastructure working with operating systems, SAN / NAS, Containers, Identity & Access management, Data Security life cycle, virtualization platforms, cloud environments and other critical infrastructure components will be preferred.
- Other Skills / Expertise / Knowledge Required:
- Understanding of Information Security Architecture.
- Awareness of risk frameworks and infrastructure security-related risks.
- Understanding of essential infrastructure security-related security tools and techniques.
- Good interpersonal skills and an active team player.
- Ability to prioritize and meet strict deadlines.
- Outline of Main Duties / Responsibilities:
- To manage and continuously enhance the organization’s Infrastructure Security Program, ensuring alignment with business objectives, cybersecurity strategy, regulatory requirements, and industry best practices.
- To manage security architecture reviews for infrastructure projects and provide strategic guidance on secure design principles for servers, virtualization platforms, cloud services, storage systems, and enterprise network infrastructure.
- To manage infrastructure security assessment activities, including Vulnerability Assessments (VA), configuration compliance reviews, penetration testing coordination, CIS benchmark assessments, operating system hardening and security validation of servers, cloud infrastructure, virtualization platforms and enterprise systems.
- To prepare and maintain infrastructure vulnerability MIS, track remediation activities, and ensure timely closure of identified security findings in accordance with organization’s risk management requirements.
- To prepare infrastructure security assessment reports, vulnerability dashboards, compliance reports and management summaries for periodic review by senior management.
- To define, implement, and maintain infrastructure security governance, policies, standards, procedures and security baselines for servers, operating systems, ATMs, virtualization platforms, cloud environments, storage and systems infrastructure.
- To oversee infrastructure security risk assessments and ensure security risks are identified, evaluated, treated, and mitigated before deployment into production environments.
- To lead the implementation and enforcement of secure infrastructure hardening standards based on recognized benchmarks (e.g., CIS Benchmarks) across the bank’s environment.
- To coordinate with IT Infrastructure, Systems, Cloud, Database, System Administration and other technology teams to ensure secure controls are effectively implemented and maintained across the infrastructure.
- To ensure secure configuration, hardening, continuous monitoring and compliance of enterprise infrastructure, including Windows and Linux servers, databases, virtualization platforms, cloud workloads, storage systems and Active Directory.
- To support internal and external audits by providing infrastructure security governance, compliance documentation, remediation status, and technical guidance.
- To perform any other assignment as assigned by the supervisor(s).
- Assessment Interview(s): Only shortlisted candidates strictly meeting the above-mentioned basic eligibility criteria will be invited for panel interview(s).
- Employment Type: The employment will be on contractual basis for three years which may be renewed on discretion of the Management. Selected candidates will be offered compensation package and other benefits as per Bank’s Policy / rules.
Interested candidates may visit the website https://nbp.rozee.pk/ and apply online within 10 working days from the date of publication of this advertisement as per given instructions.
Applications received after due date will not be considered in any case. No TA / DA will be admissible for interview.
National Bank of Pakistan is an equal opportunity employer and welcomes applications from all qualified individuals, regardless of gender, religion, or disability.
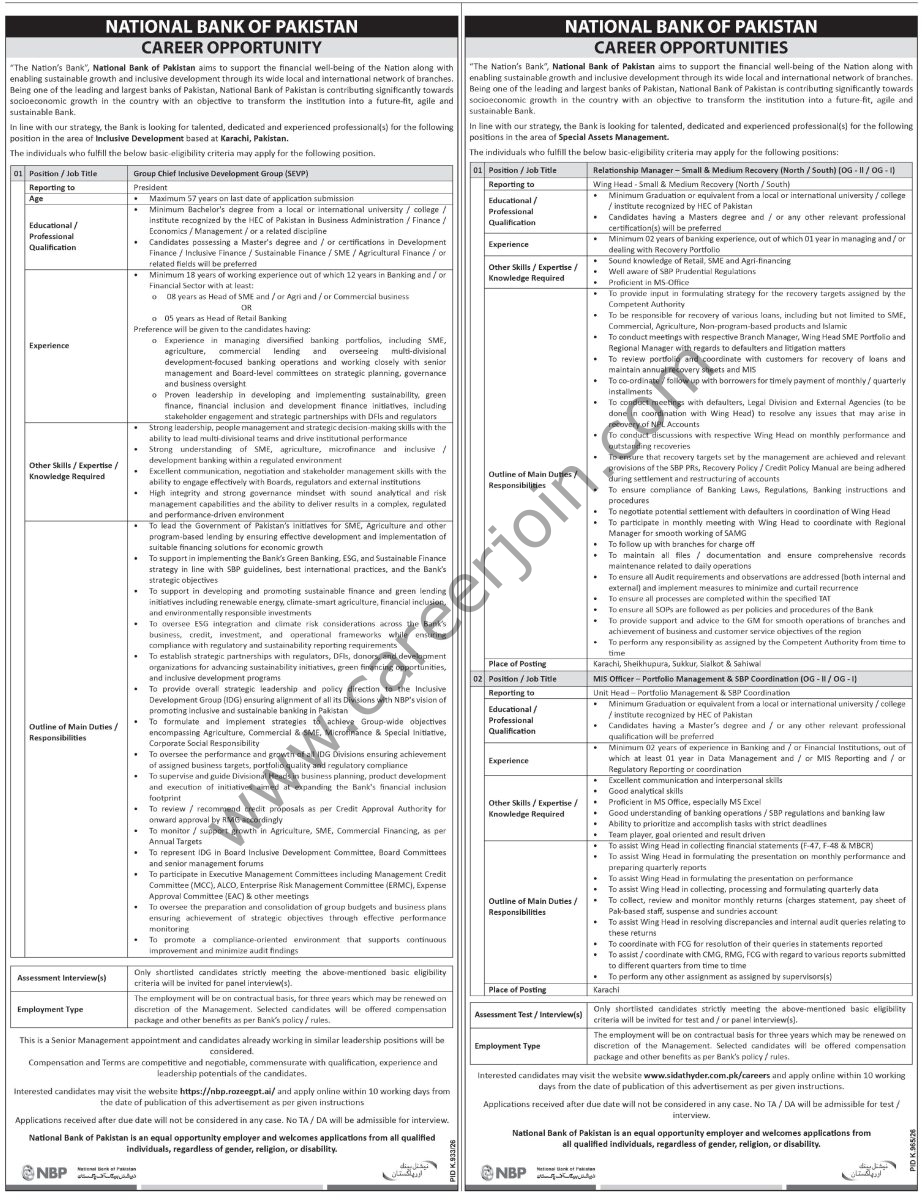
The National Bank of Pakistan (NBP) aims to enhance national financial well-being while supporting sustainable growth and inclusive development across its extensive network. As one of Pakistan’s premier banking institutions, NBP is actively driving socioeconomic progress while evolving into a future-fit, agile, and sustainable organization. In alignment with this vision, NBP is hiring experienced professionals for its Inclusive Development Group, based in Karachi.
01. Position: Group Chief Inclusive Development Group (SEVP)
- Reporting Line: Reports directly to the President.
- Age Limit: Maximum 57 years old as of the application submission deadline.
- Educational Background:
- Requires a minimum of a Bachelor’s degree from an HEC-recognized local or international institution in Business Administration, Finance, Economics, Management, or a related discipline.
- Candidates possessing a Master’s degree or specialized certifications in areas such as Development Finance, Inclusive Finance, Sustainable Finance, SME, or Agricultural Finance will be given preference.
- Required Experience:
- Must have a minimum of 18 years of total work experience, including 12 years within the banking or financial sector.
- The candidate must possess either 8 years of leadership experience as Head of SME, Agri, or Commercial business, OR 5 years of experience as Head of Retail Banking.
- Preference will be extended to individuals with experience overseeing multi-divisional development-focused operations, leading sustainability and green finance initiatives, and building strategic partnerships with regulators and DFIs.
- Key Skills & Competencies: Strong strategic decision-making, people management, and leadership skills. In-depth understanding of SME, agricultural, microfinance, and development banking within regulated environments, coupled with high governance and risk management standards.
- Core Responsibilities:
- Lead government-backed initiatives for SME, agricultural, and program-based lending to drive economic growth.
- Implement NBP’s Green Banking, ESG, and Sustainable Finance strategies according to State Bank of Pakistan (SBP) guidelines.
- Provide overall strategic guidance to the Inclusive Development Group (IDG) and oversee the performance of all its underlying divisions.
- Review and recommend credit proposals per approval authorities and participate in key executive committees such as ALCO, MCC, and ERMC.
- Drive compliance, risk mitigation, and continuous operational improvement across group activities.
Application & Employment Details
- Assessment: Shortlisted applicants meeting the basic eligibility requirements will be invited for panel interviews.
- Employment Structure: Offered as a 3-year renewable contractual position, featuring a competitive compensation package aligned with market standards and internal bank policies.
- Application Process: Eligible candidates can apply online by visiting https://nbp.rozeegpt.ai/ within 10 working days of the advertisement’s publication.
- General Terms: Late applications will not be processed, and no TA/DA is provided for interviews. NBP is an equal opportunity employer.
Overview and Mission NBP is seeking qualified and dedicated professionals for key positions within its Special Assets Management division.
01. Position: Relationship Manager – Small & Medium Recovery (North / South) (OG-II / OG-I)
- Reporting Line: Reports to the Wing Head – Small & Medium Recovery (North / South).
- Educational Qualification: Requires at least a Graduation degree or equivalent from an HEC-recognized institution. Master’s degree holders or those with relevant professional certifications are preferred.
- Experience: Minimum of 2 years in banking, with at least 1 year specifically managing or handling recovery portfolios.
- Key Skills: Sound understanding of Retail, SME, and Agri financing, familiarity with SBP Prudential Regulations, and proficiency in MS Office.
- Core Responsibilities:
- Contribute to recovery strategies and handle loan recovery across SME, Commercial, Agriculture, Islamic, and non-program products.
- Coordinate with Branch Managers, Regional Managers, Legal Divisions, and external agencies to resolve non-performing loan (NPL) matters.
- Ensure full adherence to SBP regulations, internal credit policies, and legal standards during account restructurings or settlements.
- Maintain recovery logs, perform regular follow-ups with borrowers, and manage operational documentation.
- Posting Locations: Karachi, Sheikhupura, Sukkur, Sialkot, and Sahiwal.
02. Position: MIS Officer – Portfolio Management & SBP Coordination (OG-II / OG-I)
- Reporting Line: Reports to the Unit Head – Portfolio Management & SBP Coordination.
- Educational Qualification: Graduation degree or equivalent from an HEC-recognized university, with preference given to Master’s degree holders.
- Experience: At least 2 years in banking or financial institutions, with a minimum of 1 year focused on data management, MIS reporting, or regulatory coordination.
- Key Skills: Strong analytical capabilities, excellent interpersonal skills, advanced proficiency in MS Excel/Office, and a solid grasp of SBP regulations.
- Core Responsibilities:
- Assist the Wing Head in compiling financial statements (including F-47, F-48, and MBCR) and preparing performance presentations and quarterly reports.
- Collect, review, and monitor monthly returns, staff pay sheets, charges statements, and suspense accounts.
- Coordinate with internal departments (such as FCG, CMG, and RMG) and external bodies to resolve audit queries and statement discrepancies.
- Posting Location: Karachi.
Application & Employment Details
- Assessment: Shortlisted candidates meeting all eligibility criteria will be invited for testing and/or panel interviews.
- Employment Structure: Contractual arrangement for an initial period of 3 years, renewable based on management discretion.
- Application Process: Candidates should apply online at https://www.sidathyder.com.pk/careers/ within 10 working days of publication.
- General Terms: Incomplete or late applications will be rejected. No TA/DA will be reimbursed for assessment tests or interviews. NBP operates as an equal opportunity employer.
Published Date: 20 September 2026
Newspaper: Dawn / Express Tribune
National Bank NBP Jobs September 2026


Jobs By Cities
Jobs By Field
Jobs By Organization
